About TruffleHog
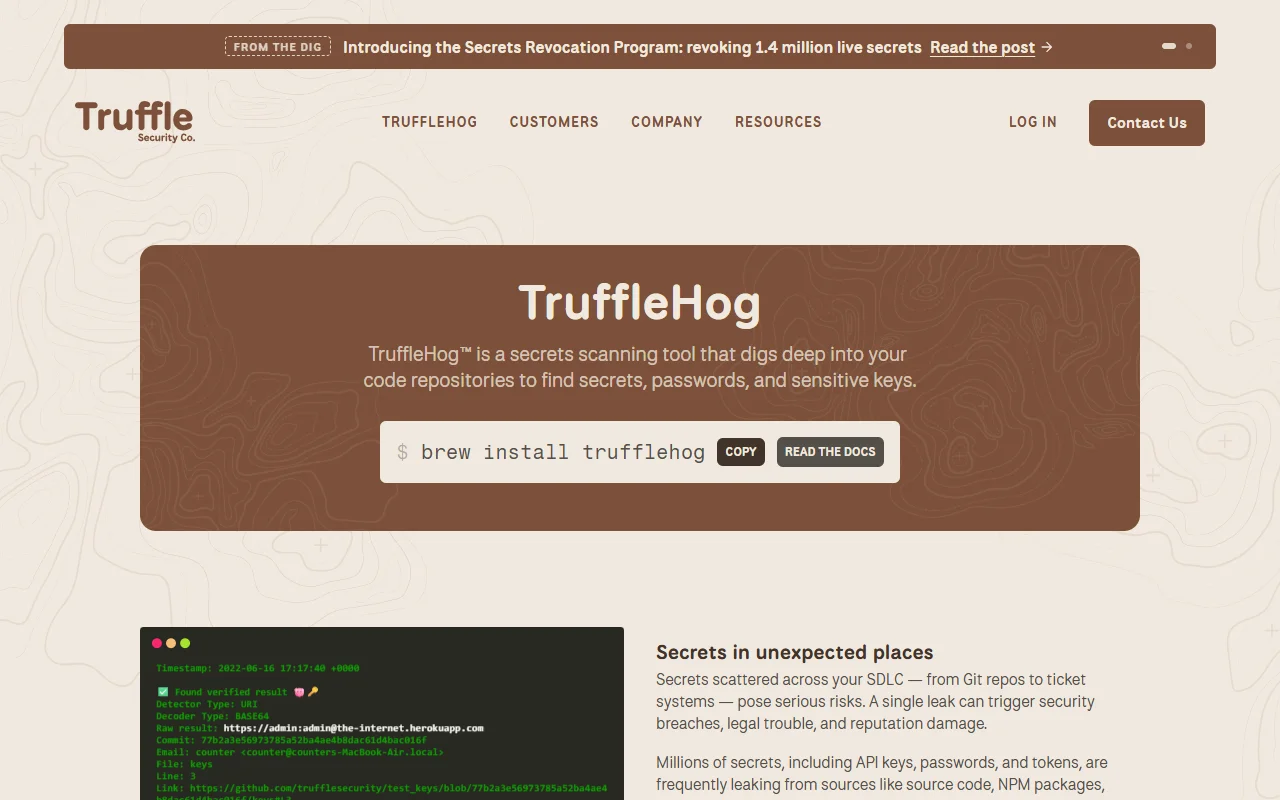
TruffleHog is an open source secrets scanner from Truffle Security. It searches code repositories for passwords, tokens and keys that were committed by mistake.
What it does
The tool digs through repository history, not only the latest files, so old commits that contain secrets are found too. For many key types it can check whether a secret is still active, which helps teams focus on keys that could actually be abused. Each result shows the file, line and commit where the secret appears, along with rotation guidance for some key types.
Key features
- Scans Git repositories for passwords and API keys
- Can filter results to secrets it has verified as live
- Installs with a package manager such as Homebrew
- Shows the file, line and commit for each finding
- Gives rotation guides for some key types
Who it's for
TruffleHog suits security teams, developers and DevOps engineers who want to catch secrets before they leak, or during audits. Teams that only need to check one small repository by hand may find simpler tools enough.
Pricing and good to know
TruffleHog is open source under the AGPL-3.0 license. That is a strong copyleft license, so companies that change and host the tool should check its terms first. The vendor site also has customer and log in pages, so a paid offering may exist alongside the open source tool.
Highlights
- Scans Git repositories for passwords and API keys
- Can filter results to secrets it has verified as live
- Installs with a package manager such as Homebrew
- Shows the file, line and commit for each finding
- Gives rotation guides for some key types