About Checkmarx
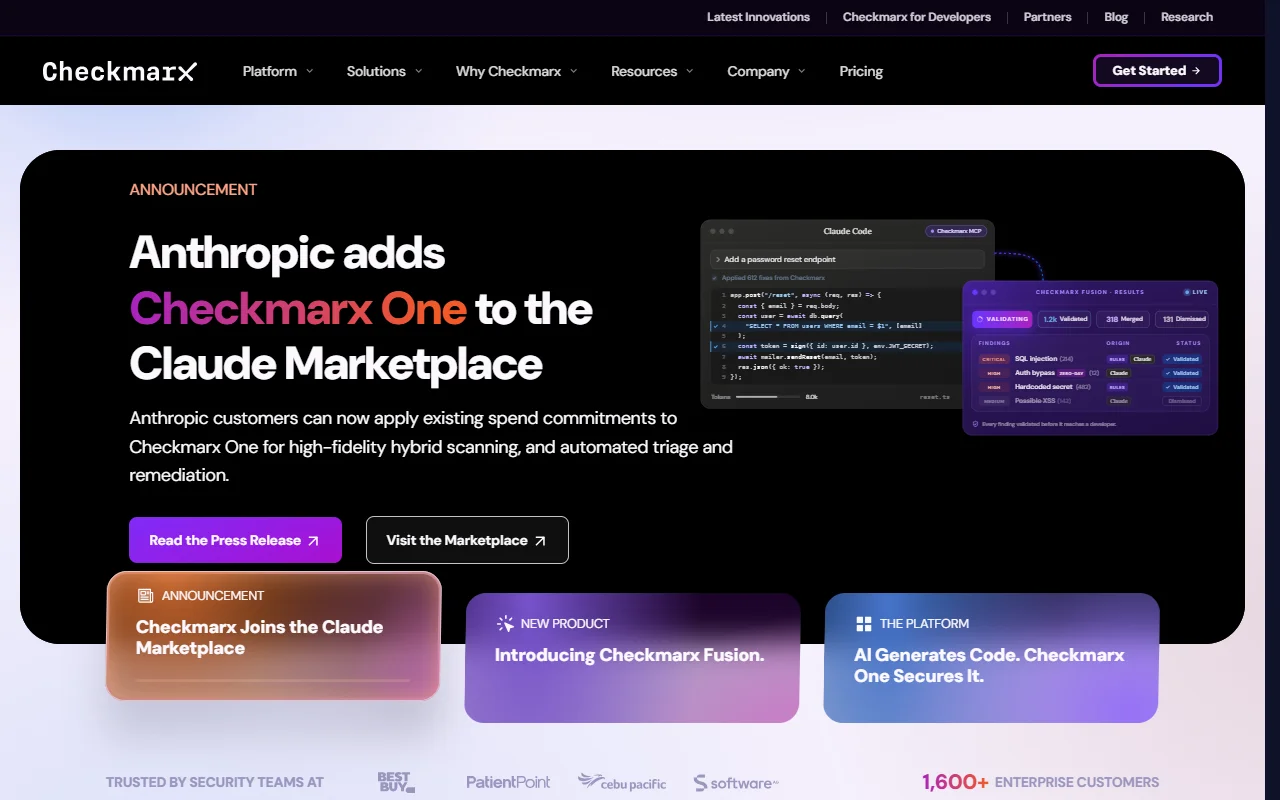
Checkmarx is an application security platform aimed at large engineering organizations. It scans source code, dependencies and running applications so security teams can find and rank the issues that matter most.
What it does
Checkmarx brings several scanning methods, including static analysis of source code, into one platform. Its AI agents help teams sort through findings and suggest fixes, and the platform tracks risk from code through to runtime. The stated goal is to cut noise in scan results, so developers spend less time on false alarms and more time on real problems.
Key features
- Static analysis of source code
- Automated triage of findings
- Suggested fixes for vulnerabilities
- Tracking of AI assets and MCP servers
- Risk view from code to runtime
Who it's for
Checkmarx suits enterprise security and development teams that need to govern many repositories and meet compliance rules. It is less suited to solo developers or small projects that only need a free scanner for a single repository.
Pricing and good to know
The website has a pricing page, but no plan amounts appear in the text we read, so check it for current terms. Checkmarx is sold as an enterprise product, which means the buying process is usually longer than for a self-serve tool. Teams should confirm which languages and frameworks are covered before rolling it out.
Highlights
- Static analysis of source code
- Automated triage of findings
- Suggested fixes for vulnerabilities
- Tracking of AI assets and MCP servers
- Risk view from code to runtime