About CodeQL
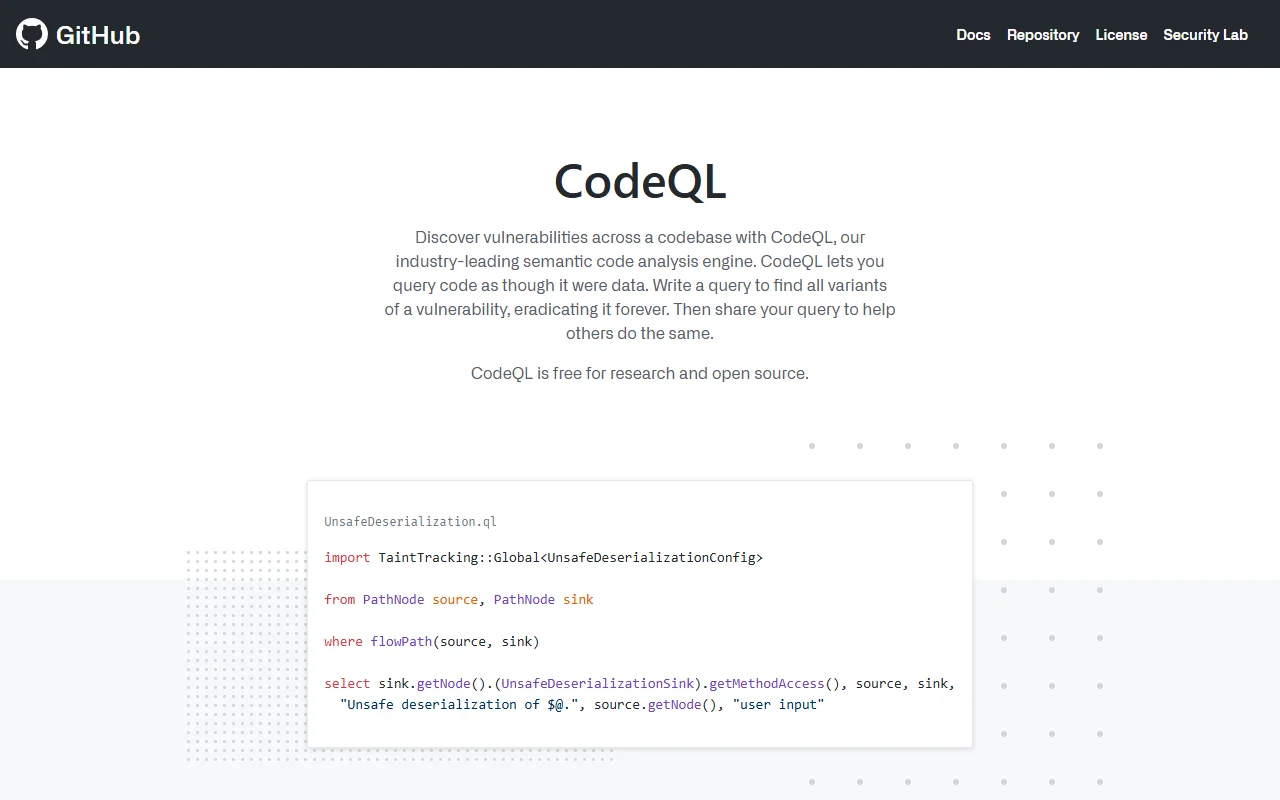
CodeQL is an open source semantic code analysis engine from GitHub. It lets you write queries that search a codebase for vulnerability patterns and for other variants of the same bug.
What it does
You build a database from a project's code, then run queries against that database to find matching code paths. The queries are written in a dedicated query language that treats code as data, which makes it possible to follow user input through the program to risky calls. Once a query works, you can share it so other people can search for the same bug class in their own projects.
Key features
- Queries code as if it were data
- Finds all variants of a known vulnerability pattern
- Runs queries from Visual Studio Code
- Shares reusable queries with others
Who it's for
CodeQL suits security researchers, bug hunters and security engineers who want custom checks that go beyond standard scanners. Teams that only need a quick scanner for common issues may find ready-made tools faster to start with.
Pricing and good to know
CodeQL is free for research and open source projects, and the repository is published under the MIT license. Use on private code may have different terms, so read the CodeQL terms before adopting it at work. Writing good queries takes time, and the learning curve is steeper than for a point-and-click scanner.
Highlights
- Queries code as if it were data
- Finds all variants of a known vulnerability pattern
- Runs queries from Visual Studio Code
- Shares reusable queries with others