About OSV-Scanner
OSV-Scanner is a free command line tool from Google that checks a project's dependencies against the OSV vulnerability database. It is an officially supported front end to that open database.
What it does
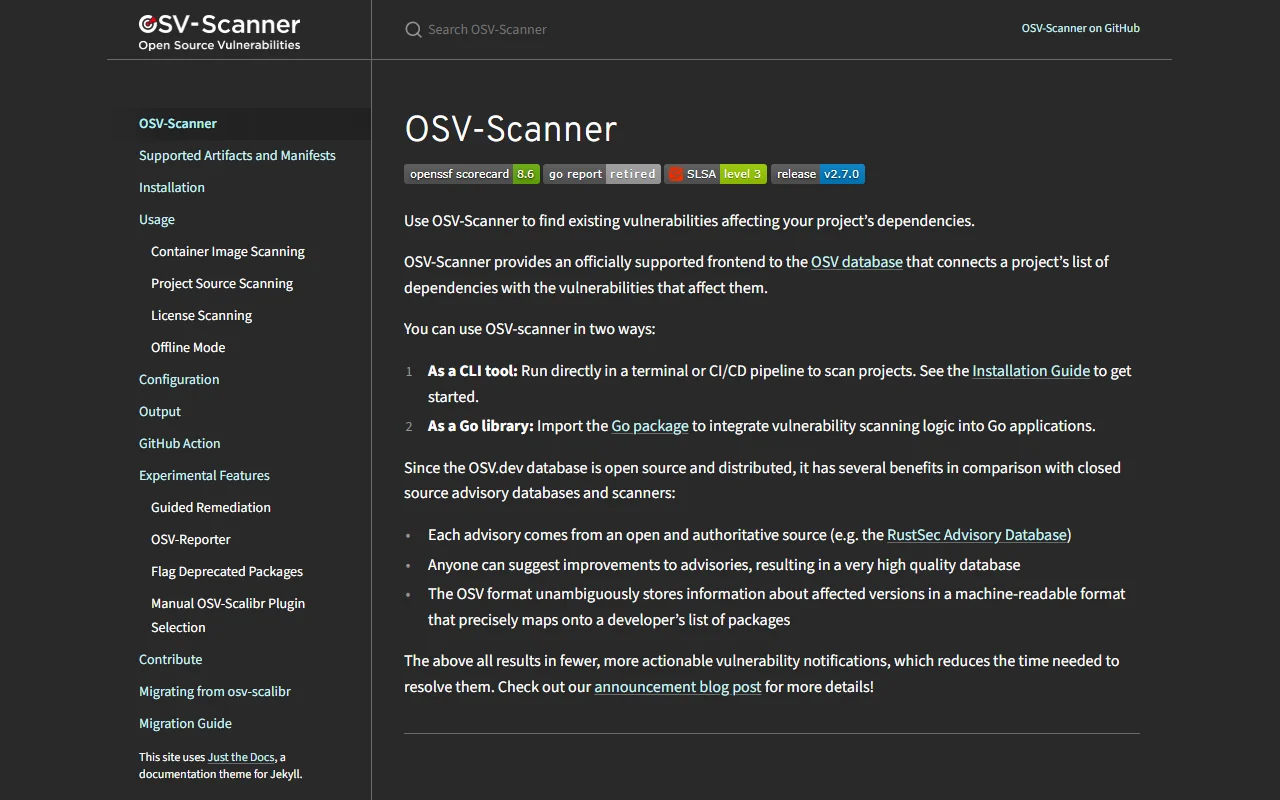
The tool reads the dependency manifests in your project and matches each package and version against known advisories. OSV stores affected versions in a machine-readable format, which the project says leads to fewer and more actionable alerts. You can run the scanner by hand in a terminal or inside a CI/CD pipeline, and it can also be imported as a Go package.
Key features
- Scans dependency lists for known vulnerabilities
- Runs in a terminal or CI/CD pipeline
- Scans container images
- Checks licenses of dependencies
- Can be used as a Go library
Who it's for
OSV-Scanner fits developers and platform teams who want a free dependency check built into their build process. It works best on projects with clear manifest files, since it relies on the package lists it finds in them.
Pricing and good to know
OSV-Scanner is open source under the Apache-2.0 license, and the OSV database it queries is open to anyone. The project's guides cover installation, usage, offline mode and a GitHub Action. Running the scanner in offline mode needs a local copy of the data, so plan for that if your build servers have no internet access.
Highlights
- Scans dependency lists for known vulnerabilities
- Runs in a terminal or CI/CD pipeline
- Scans container images
- Checks licenses of dependencies
- Can be used as a Go library