About SonarQube
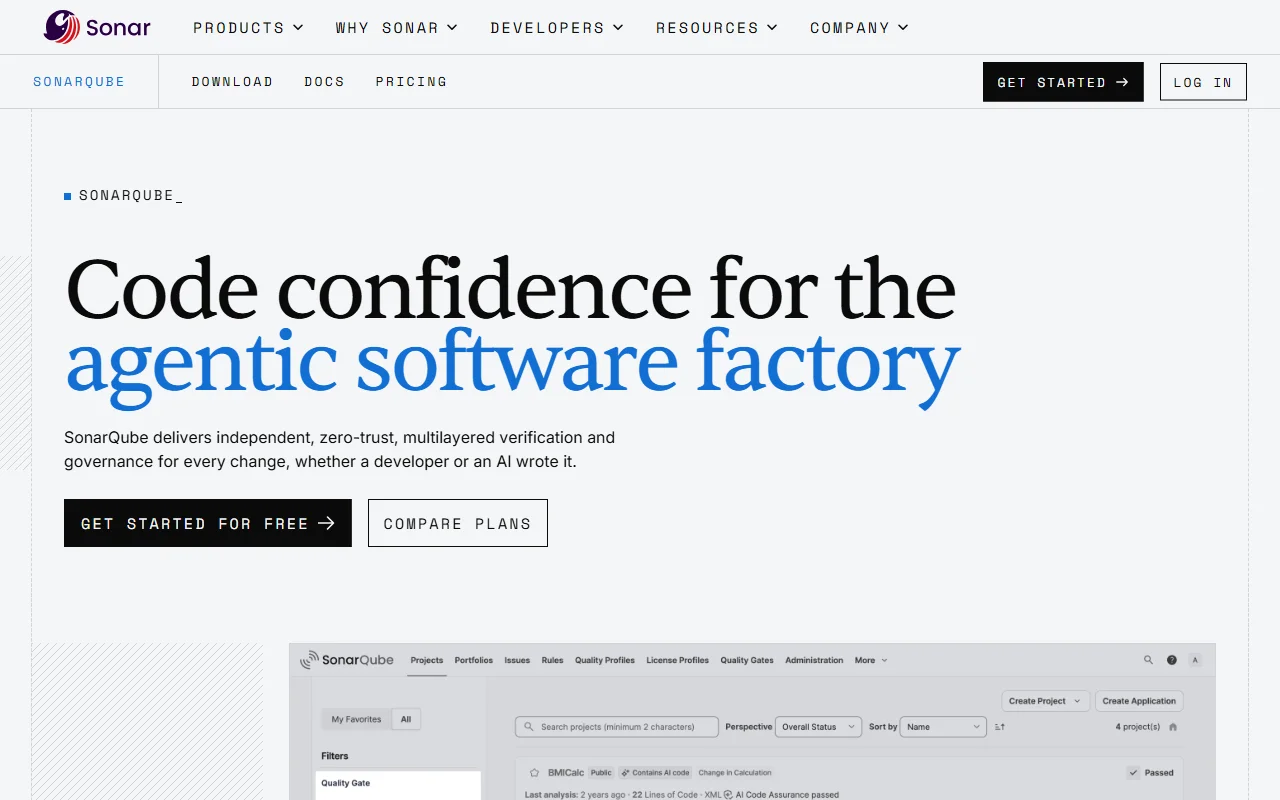
SonarQube is a code analysis product from Sonar that checks code for quality, reliability and security. It reviews every change, whether a person or an AI tool wrote it.
What it does
SonarQube reviews pull requests and code changes for reliability, security and maintainability issues. Quality gates decide which changes can merge, and each result is time-stamped and tied to its commit, so teams can review what was checked later. It connects to IDEs and coding tools through plugins, a command-line tool and MCP support, so the same standards apply wherever code is written.
Key features
- Reviews each pull request for issues
- Quality gates control which changes merge
- Keeps time-stamped records tied to each commit
- Connects to IDEs and coding agents through plugins
- Runs as a cloud service or on your own servers
Who it's for
Engineering teams and tech leads who set coding standards and want them enforced automatically are the main audience. Teams with audit needs may also find it useful, because checks are recorded against commits.
Pricing and good to know
SonarQube offers a free way to get started, and the site links to a plan comparison for paid options. The cloud version is fully managed by Sonar, while the server version runs inside your own infrastructure. Check the plan comparison for current limits and features before choosing a deployment.
Highlights
- Review each pull request for reliability and security issues
- Block merges when quality gates fail
- Keep time-stamped records tied to each commit
- Connect to IDEs and coding agents through plugins
- Run as a cloud service or on your own servers