About Gitleaks
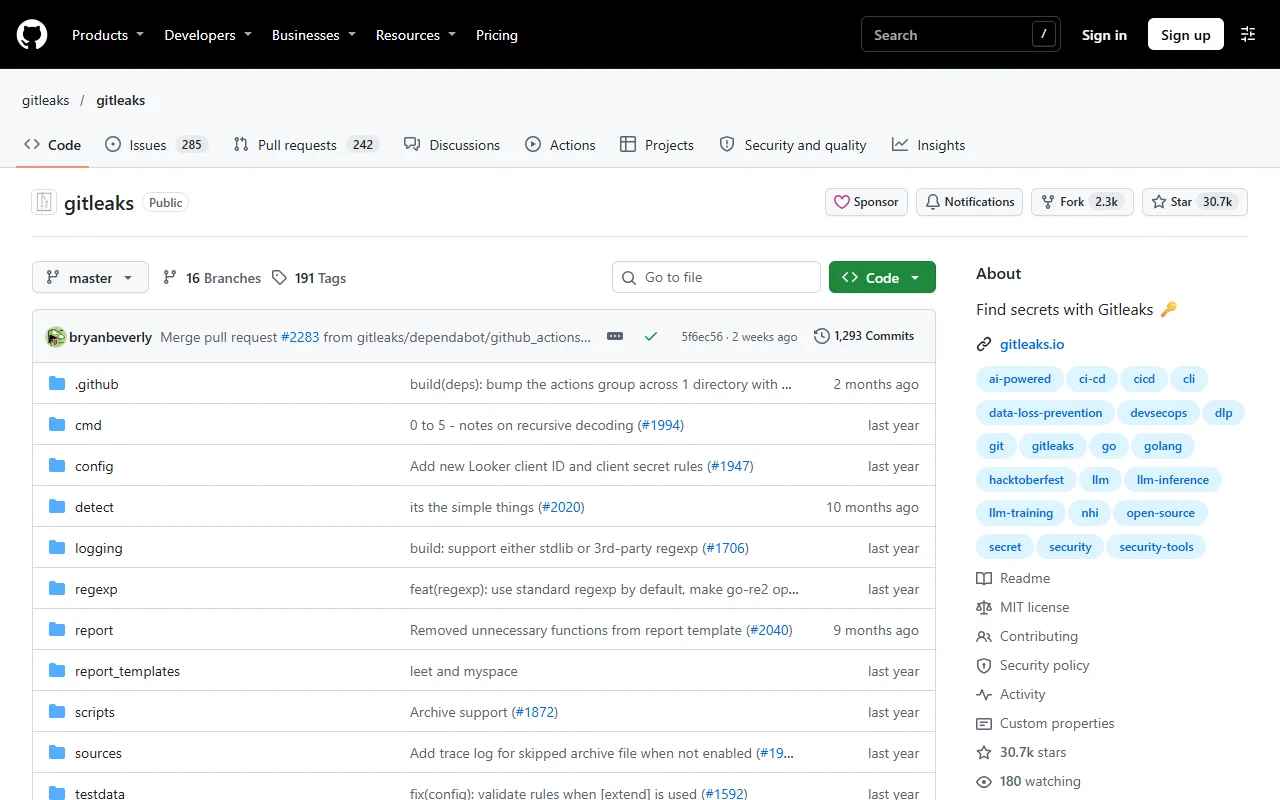
Gitleaks is a command-line tool that scans git repositories for secrets such as passwords and API keys. It can run on a developer's machine, in a build pipeline, or as a pre-commit check.
What it does
Gitleaks looks through the files and history of a git repository and reports strings that match secret patterns. It ships with a set of default rules, and a config file lets you add your own rules or allowlist results that are known to be safe. The tool is written in Go and can be used in local work and in automated checks alike.
Key features
- Scans git history and current files
- Uses built-in rules for common secret types
- Adds custom rules and allowlists in a config file
- Runs as a pre-commit hook
- Writes scan reports for review
Who it's for
Developers who want to catch leaked credentials before they reach a shared repository are the main audience. Security teams and DevOps engineers can also add it to CI pipelines to check every change.
Pricing and good to know
Gitleaks is released under the MIT license, so it is free to use. The maintainer has said the project is feature complete, and future releases will be security fixes only. Plan for that when you depend on it, and check the repository for recent activity.
Highlights
- Scan git history and current files for secrets
- Use built-in rules for common secret types
- Add custom rules and allowlists in a config file
- Run as a pre-commit hook before code is committed
- Write scan reports for review