About Seq
Seq is a self-hosted log server for structured logs. It collects events from your applications and lets you search, filter and alert on them in real time, while the data stays inside your own infrastructure.
What it does
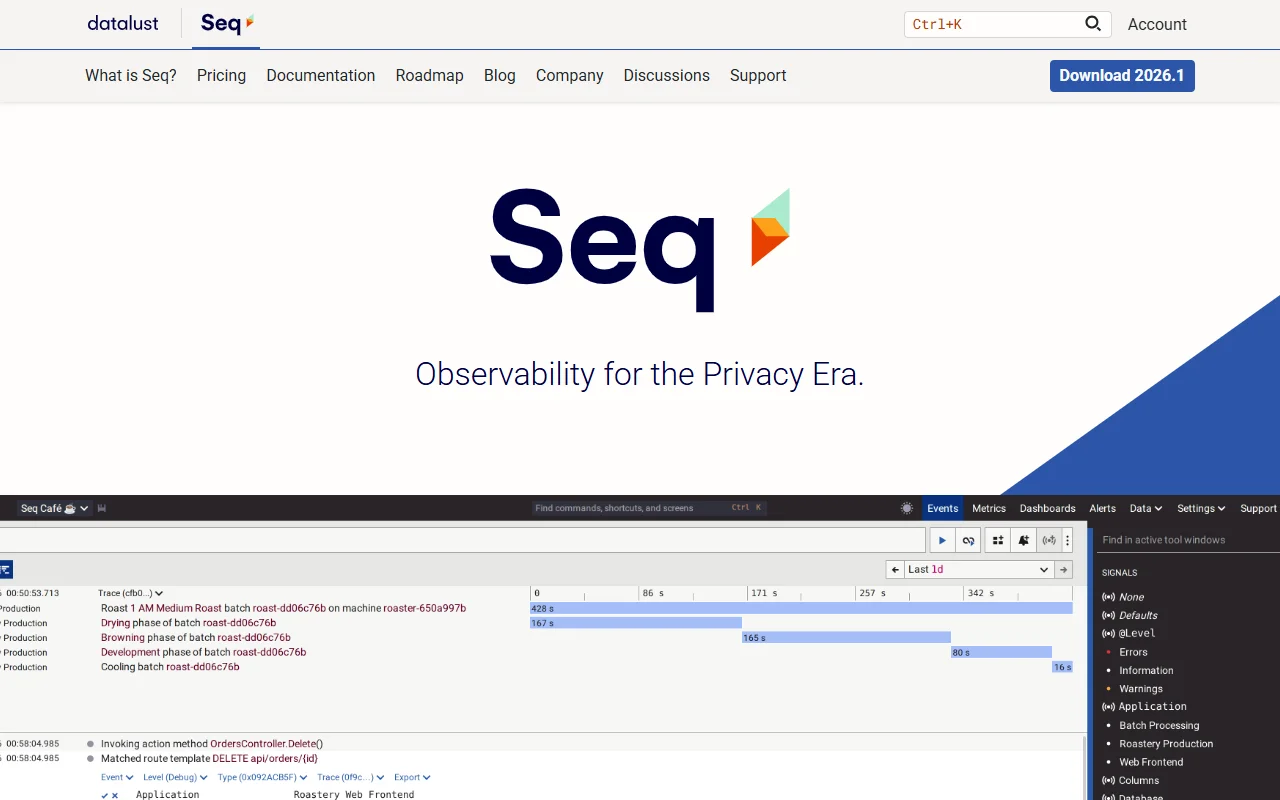
Seq receives structured log events, traces and metrics, and presents them in one interface. You can filter and pivot on log fields, follow a request across services, and set alerts on custom conditions. Alerts can be sent to channels such as Slack, Teams and email. A command line tool and an MCP integration let you connect Seq to other tools, which helps with live debugging and triage.
Key features
- Search and filter structured log events
- Follow traces to find slow requests
- See metrics next to your logs
- Send alerts to Slack, Teams or email
- Command line and MCP integration
Who it's for
Developers and operations teams that run their own applications and want logs kept in their own infrastructure. It suits teams with strict privacy or data residency needs.
Pricing and good to know
Seq is self-hosted, so you run it on your own servers, and you control where the data is stored. The company states that there are no subprocessors and that it does not train models on customer data. Pricing and licence terms are published on the company's website, so review them before you deploy.
Highlights
- Filter and pivot on structured log events
- Follow traces to find slow requests
- Monitor metrics alongside logs
- Send alerts to Slack, Teams or email
- Work with the command line tool or MCP integration