About mitmproxy
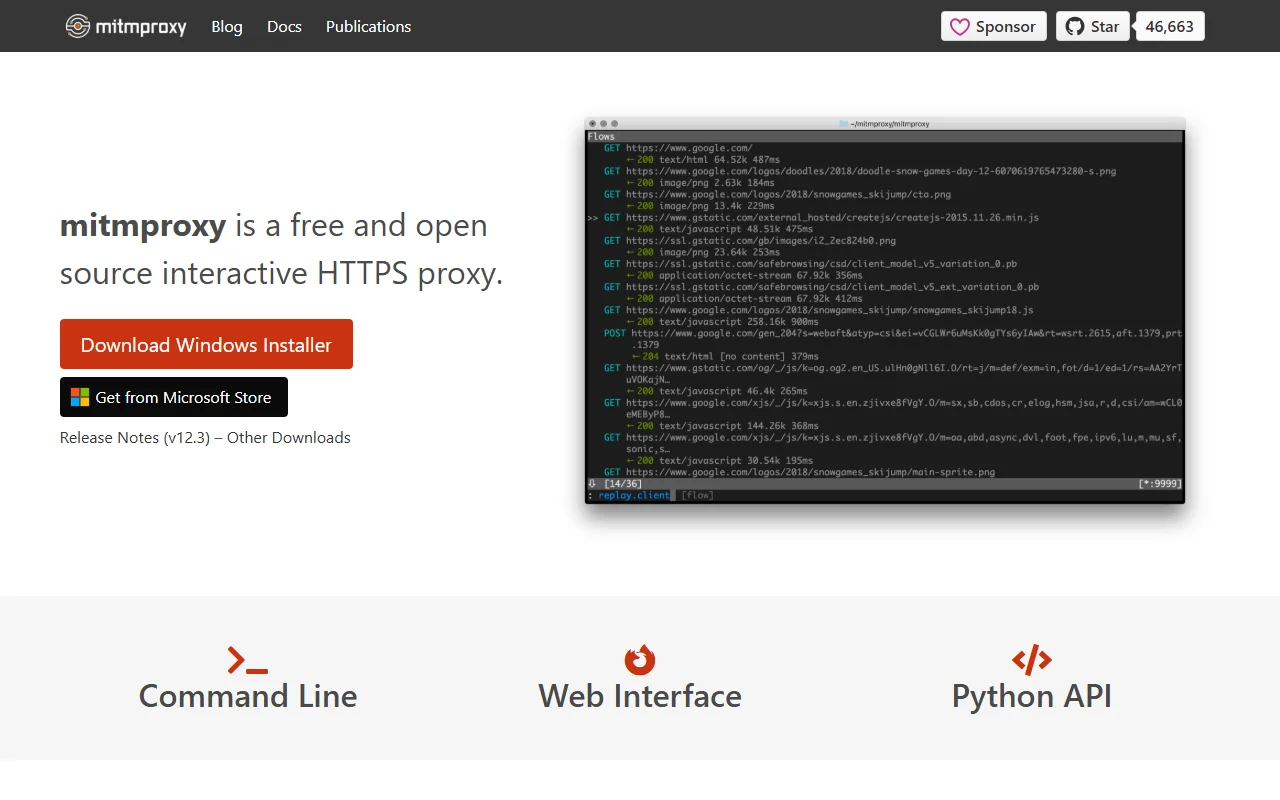
mitmproxy is a free, open source interactive HTTPS proxy. It lets you intercept, inspect, modify and replay web traffic passing between a client and a server.
What it does
mitmproxy sits between a client and a server and shows the messages that pass through. It handles HTTP/1, HTTP/2, HTTP/3 and WebSockets, as well as other TLS-protected protocols. You can decode message types ranging from HTML to Protobuf, change a message before it reaches its destination, or replay it later. The web interface, mitmweb, gives a view similar to browser developer tools, and a Python API lets you write addons that automate changes.
Key features
- Intercept and inspect HTTP and WebSocket traffic
- Modify messages before they reach the server
- Replay requests to a client or server
- Web interface called mitmweb
- Python API for custom addons
Who it's for
Security testers, developers and privacy researchers who need to see exactly what an app sends over the network. The tool is used for debugging, testing and penetration testing.
Pricing and good to know
mitmproxy is free and licensed under MIT. It runs from the command line, and a web interface is also available. Use it only on traffic you are allowed to inspect, because it can decrypt HTTPS sessions when the device trusts its certificate.
Highlights
- Intercept and inspect HTTP and WebSocket traffic
- Modify messages before they reach the server
- Replay requests to a client or server
- Use the mitmweb browser interface
- Write Python addons to automate changes