About Kyverno
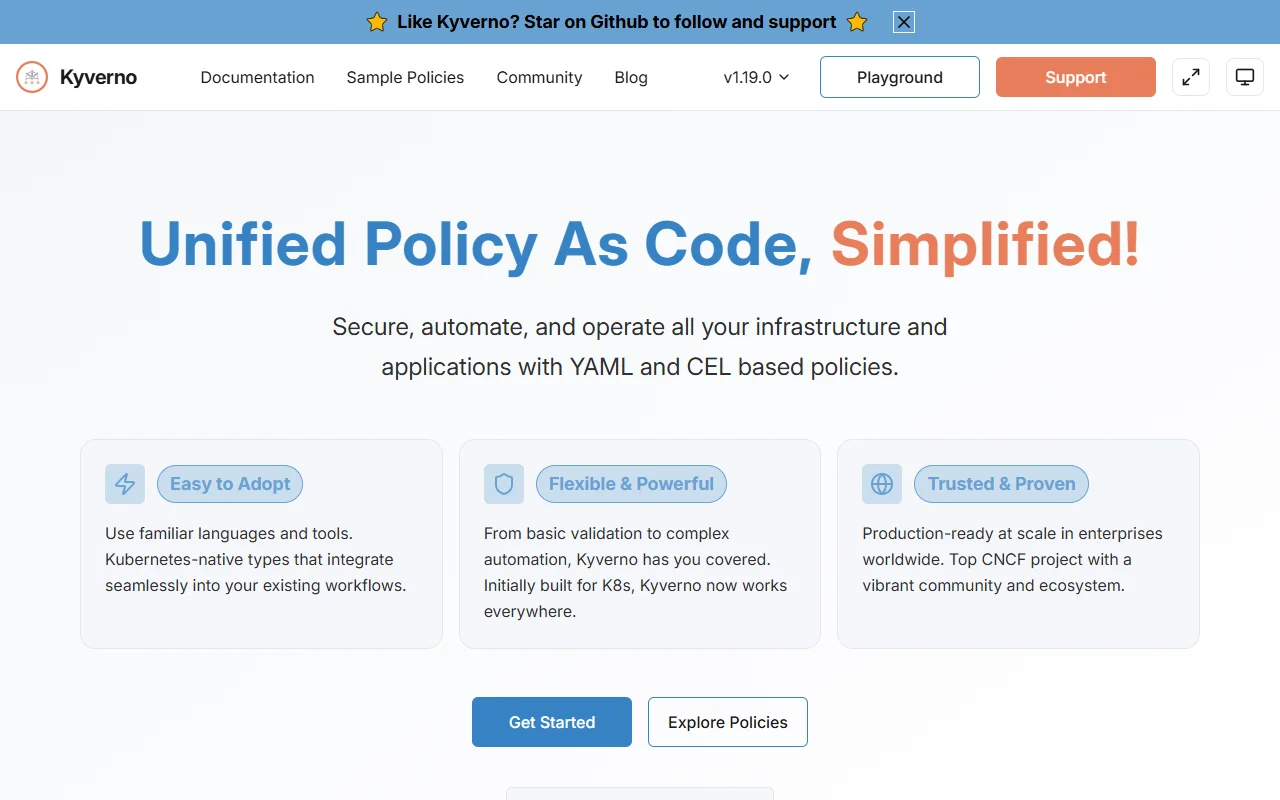
Kyverno is a policy engine for Kubernetes clusters. It lets teams write rules in YAML that check, change or create resources, and it is a CNCF project.
What it does
A Kyverno policy can require certain labels, block resources that break a standard, or change a resource as it enters the cluster. Some policies generate related objects when others are created. Kyverno runs inside the cluster and reviews requests as they come in. It also has sample policies for images, Terraform plans and Dockerfiles.
Key features
- Validates Kubernetes resources against rules
- Mutates resources, for example to add labels
- Generates related resources automatically
- Writes policies in YAML with CEL expressions
- Checks container images and Terraform plans
Who it's for
Kyverno suits platform engineers, DevOps teams and Kubernetes administrators who want policy as code. It fits teams that already use YAML and Kubernetes tools and do not want to learn a new policy language.
Pricing and good to know
Kyverno is open source under the Apache-2.0 license, and it is free to use. It runs inside a Kubernetes cluster, so you need a cluster to use it. Test new policies in a non-production cluster first, since a strict rule can block deployments.
Highlights
- Validates Kubernetes resources against rules
- Mutates resources, for example to add labels
- Generates related resources automatically
- Writes policies in YAML with CEL expressions
- Checks container images and Terraform plans