About Cloud Custodian
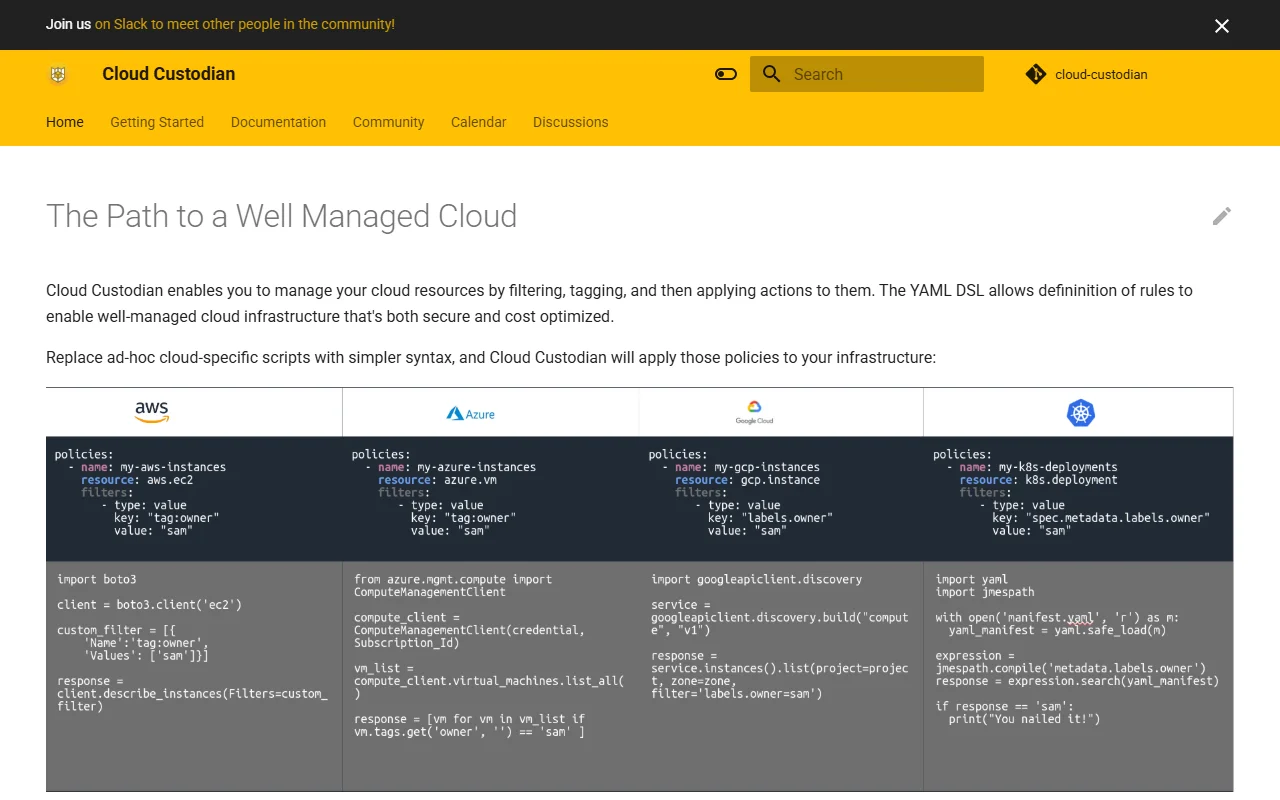
Cloud Custodian is an open source rules engine for cloud resources. You write policies in a YAML syntax to find resources, tag them and take action, such as stopping idle servers.
What it does
Each policy filters resources by their properties, then applies actions to the matches. Teams use it to enforce tagging rules, turn off resources outside working hours and remove unused items. It can run on your own machine, on a server, or as a serverless function on AWS Lambda.
Key features
- YAML policies with a simple rule syntax
- Off-hours shutdowns to save cost
- Tagging and cleanup of unused resources
- Real-time compliance enforcement
- Runs locally, on a server or on AWS Lambda
Who it's for
Cloud platform engineers, security and compliance teams, and FinOps staff who want governance defined as code. It also suits teams that already keep their infrastructure definitions in git.
Pricing and good to know
Cloud Custodian is free and open source under the Apache 2.0 license. It is a CNCF Incubating project and supports AWS, Azure and GCP. Kubernetes, Tencent Cloud and OpenStack support is in beta, and Terraform integration is in alpha.
Highlights
- Write policies in a simple YAML syntax
- Find, tag and act on resources in your cloud
- Schedule shutdowns to turn off resources out of hours
- Remove unused resources based on utilization
- Run locally, on a server or as AWS Lambda