About WPScan
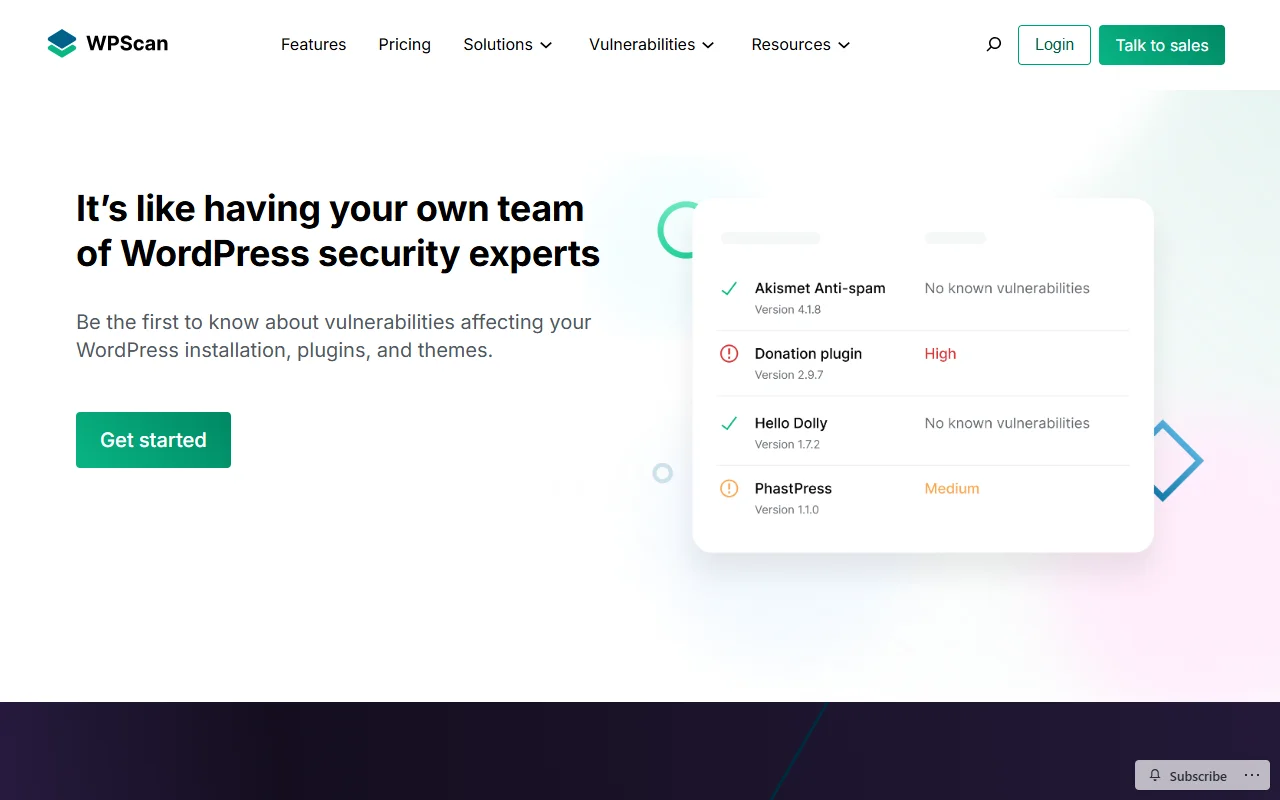
WPScan is a security tool and vulnerability database built for WordPress. It helps site owners and security teams find known weak points in WordPress core, plugins and themes.
What it does
The service keeps a large, regularly updated catalogue of WordPress security issues. You can run a quick scan of a site to get a report on its known exposure, or query the data through the API. Each entry gives enough detail to judge how serious a problem is and what to do about it.
Key features
- Catalogues over 94,000 WordPress core, plugin and theme vulnerabilities
- Free instant scan report for a site you have permission to test
- Email, Slack and webhook alerts when new issues appear
- API access to vulnerability details by ID
- Command line scanner for security researchers
Who it's for
- WordPress agencies that manage many client sites
- Site owners who want to know about plugin and theme risks
- Security researchers who run scans for non-commercial work
Pricing and good to know
A free tier covers small use, including a researcher plan capped at 25 API calls per day. Larger teams can ask for enterprise pricing based on the number of sites. Only scan sites you have permission to test, and treat the results as a starting point for review rather than a full audit.
Highlights
- Catalogues over 94,000 WordPress core, plugin and theme vulnerabilities
- Free instant scan report for a site you have permission to test
- Email, Slack and webhook alerts when new issues appear
- API access to vulnerability details by ID
- Command line scanner for security researchers