About Wireshark
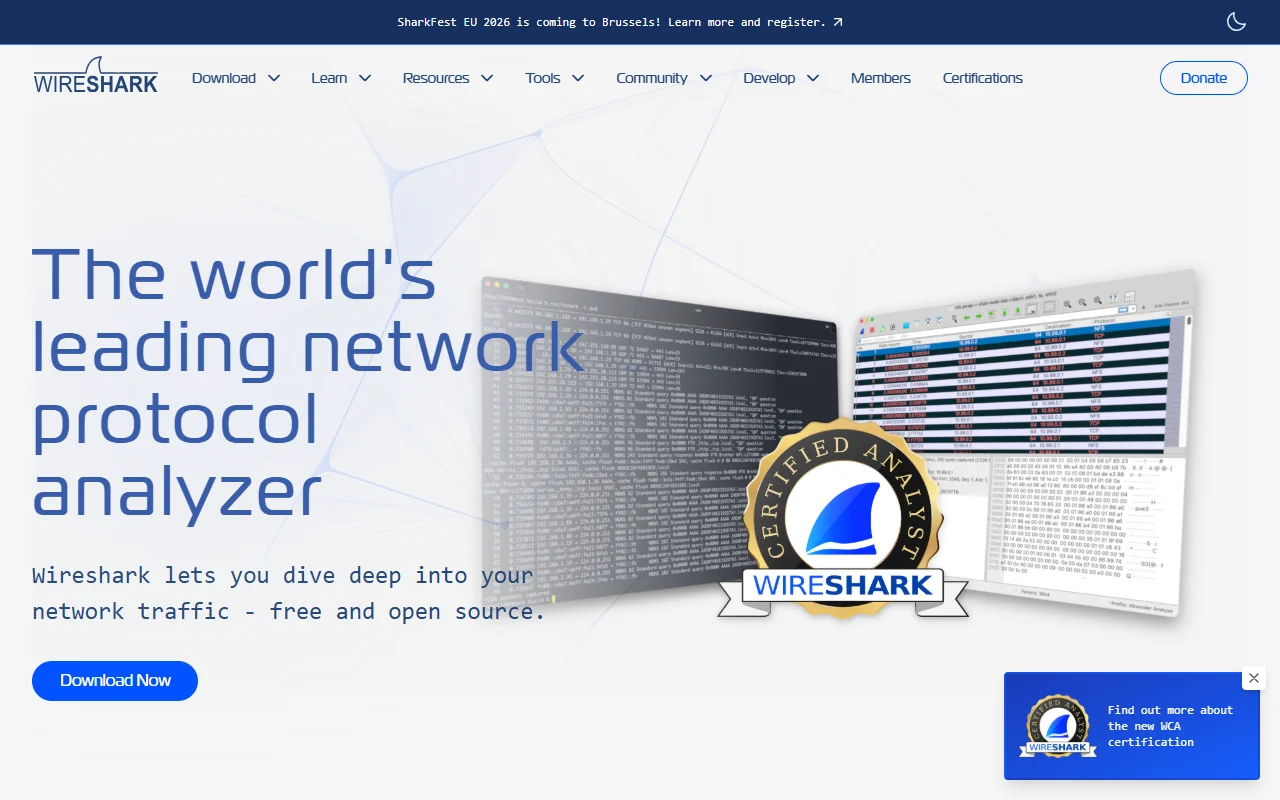
Wireshark is a free, open source network protocol analyzer. It captures network traffic and lets you browse packets in detail.
What it does
The tool captures live traffic from a network interface or opens saved capture files. It decodes hundreds of protocols and lets you filter, search and follow streams to find problems. People use it to study how an application talks on the network, or to find out why a connection is slow or failing.
Key features
- Capture live traffic from a network interface
- Open and inspect saved capture files
- Filter and search packets by protocol or field
- Follow TCP and HTTP streams
- Decode hundreds of network protocols
Who it's for
Network engineers, security analysts, developers debugging network issues and students learning how protocols work. It is a common tool in incident response and in troubleshooting slow or broken connections.
Pricing and good to know
Wireshark is free and open source, distributed under the GNU General Public License. Downloads are available for Windows, macOS and Linux. Capturing traffic on some networks may need extra permissions or a capture driver, and inspecting traffic you do not own should follow your organization's rules.
Highlights
- Capture live traffic from a network interface
- Open and inspect saved capture files
- Filter and search packets by protocol or field
- Follow TCP and HTTP streams