About Falco
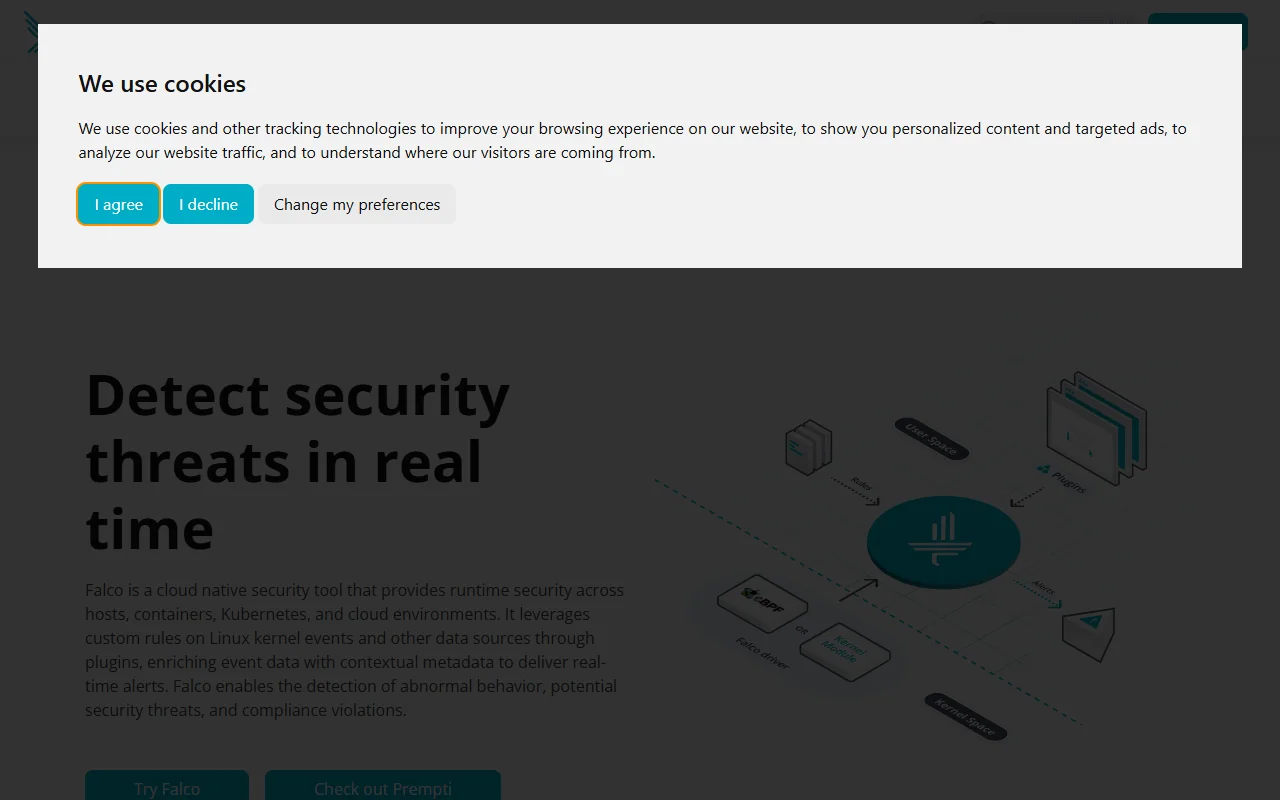
Falco is an open source, cloud native security tool that detects unusual behavior at runtime. It watches hosts, containers, Kubernetes and cloud services and raises alerts in real time.
What it does
Falco uses custom rules on Linux kernel events and other data sources, such as plugins. It adds context to each event, so alerts show what happened and where. It can detect abnormal behavior, potential threats and some compliance violations. Alerts can be forwarded to a SIEM or data lake for storage and response.
Key features
- Runtime detection using eBPF on hosts and containers
- Custom rules for kernel events and plugin data
- Kubernetes and cloud service monitoring
- Forwarding alerts to SIEM and data lake systems
- Rules that support regulatory compliance checks
Who it's for
Security engineers, platform teams and DevOps staff who run containers or Kubernetes and want to find suspicious activity as it happens. It fits teams that want to write their own detection rules.
Pricing and good to know
Falco is licensed under Apache-2.0 and developed as an open project. It runs on Linux systems. Tuning rules takes time, so expect to review alerts and adjust them for your environment.
Highlights
- Runtime detection using eBPF on hosts and containers
- Custom rules for kernel events and plugin data
- Kubernetes and cloud service monitoring
- Forwarding alerts to SIEM and data lake systems
- Rules that support regulatory compliance checks