About Promptfoo
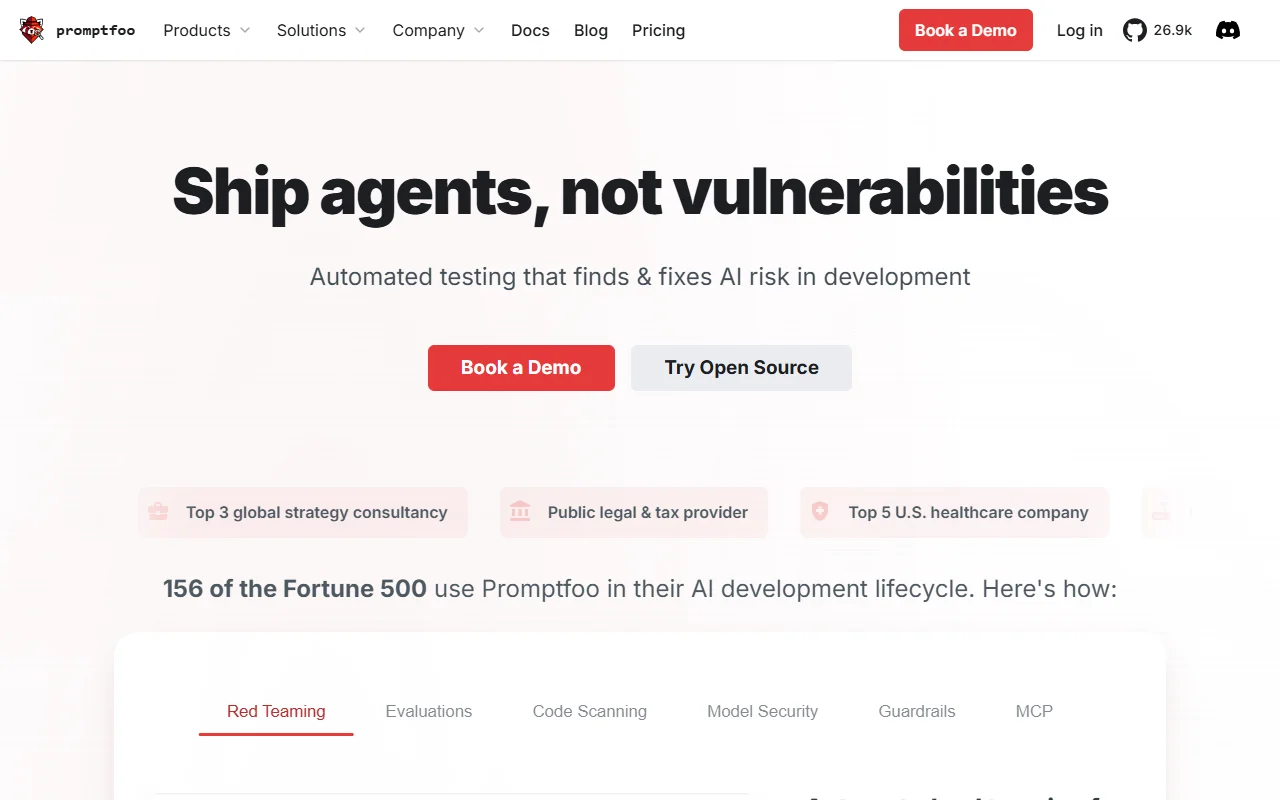
Promptfoo is an open source tool for testing prompts and finding security problems in AI applications. It runs tests from the command line and can be wired into development pipelines.
What it does
Promptfoo runs evaluations that compare prompts and models against a set of test cases. Its red teaming feature simulates attacks, such as prompt injection, jailbreaks and attempts to leak data, against an application and reports what gets through. It can also scan code and pull requests for AI risks. The team offers a commercial platform for larger organizations on top of the open source core.
Key features
- Automated red team tests against your app
- Checks for prompt injection, jailbreaks and data leaks
- Evaluations across prompts and models
- Code scanning and risk checks in pull requests
- Works with CI/CD pipelines such as GitHub and GitLab
Who it's for
The tool suits developers, QA teams and security staff who build LLM features and want tests in their normal workflow. Teams without any LLM feature in production may not need red teaming yet.
Pricing and good to know
The core tool is open source under the MIT license, and it can be started with npx. The commercial platform adds team features, reporting and support, and its pricing is set separately. Red team results depend on the attacks chosen, so a clean run is not proof that an app is secure.
Highlights
- Automated red team tests against your app
- Checks for prompt injection, jailbreaks and data leaks
- Evaluations across prompts and models
- Code scanning and risk checks in pull requests
- Works with CI/CD pipelines such as GitHub and GitLab