About CodeAnt AI
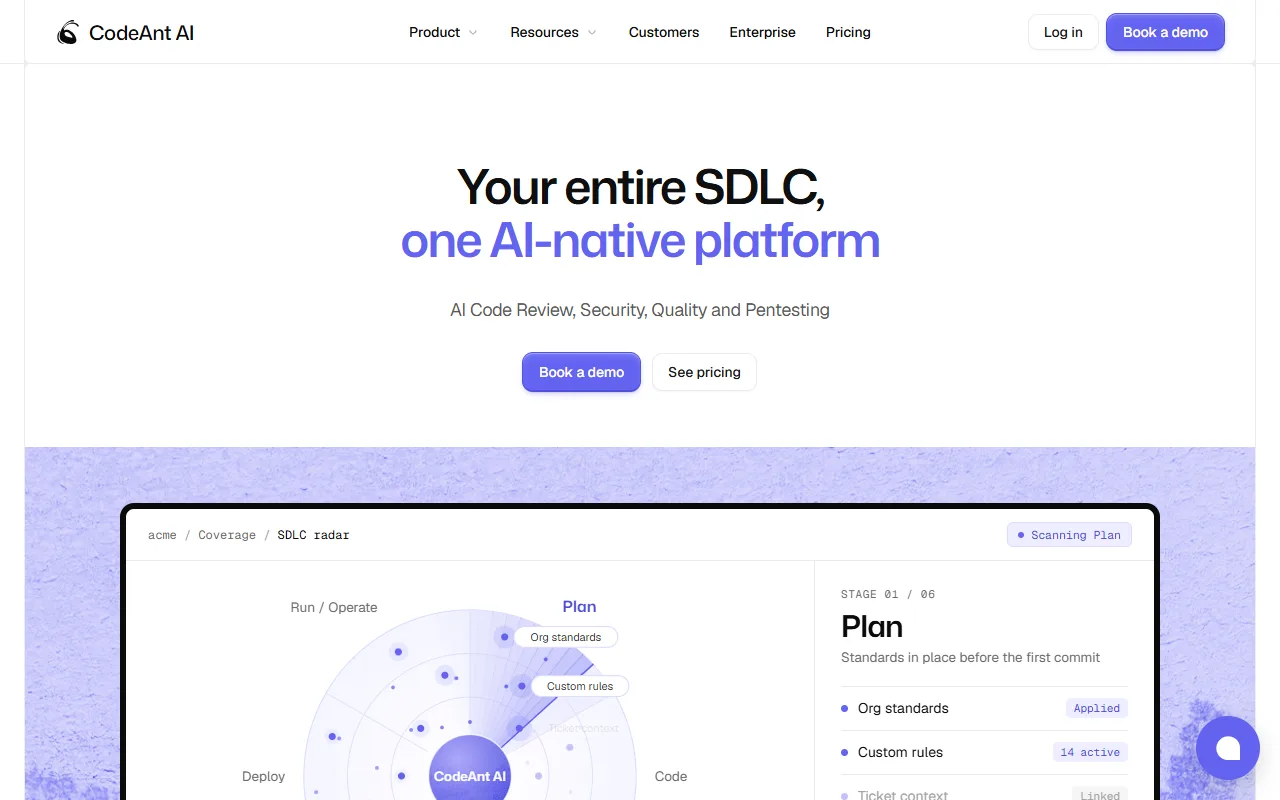
CodeAnt AI is a code review and security platform that covers the software lifecycle from pull request to deployment. It combines AI review with scanning for code, dependencies, secrets and infrastructure.
What it does
CodeAnt AI reviews every pull request for bugs and security issues before a person looks at it. It also runs static analysis, secret detection, dependency and license checks, and infrastructure-as-code and container scanning. Custom rules and quality gates can block a merge when checks fail. The site also describes DAST and pentesting options, and cloud posture and drift alerts.
Key features
- AI review of each pull request for bugs and security
- Static analysis and secret detection
- Dependency and license checks with SBOM output
- Infrastructure and container scanning
- Custom rules and quality gates for merges
Who it's for
Engineering teams that want review and security scans in one tool will find it aimed at them. Security teams that need scans across code, cloud and runtime are another likely group.
Pricing and good to know
The site has a pricing page and a book demo option, so check there for current plans. It lists integrations with the developer tools teams already use, and a compliance section. Scans add time to a pipeline, so test the quality gate settings before you let them block merges.
Highlights
- AI review of each pull request
- Static analysis and secret detection
- Dependency and license checks with SBOM
- Infrastructure and container scanning
- Custom rules and quality gates